Most customers never meet the company behind a checkout. They meet a sign-up form, a payment flow, a verification prompt and a support inbox, and they decide from those encounters whether the business deserves their card details, which means the fraud controls wrapped around those moments are doing brand work whether anyone designed them for it or not.
The tension is structural. Every control that stops a fraudster adds friction for the legitimate customer standing behind the same login screen, and the business that forgets the second person while chasing the first converts its security budget into quiet churn.
Growth teams have started treating this as their problem, correctly. Approval rates, abandonment at verification steps and the tone of a declined-payment message all move revenue, so customer trust in the security experience belongs on the same dashboard as acquisition cost.
What follows treats fraud controls as a customer experience discipline, why the threat pressure keeps rising, how proportionate friction works, why explanations convert, where layered signals beat blunt triggers, what false positives really cost and how the response after an incident decides the relationship.
Fraud Pressure Is a Growth Problem
The threat environment keeps raising the baseline. Internet crime losses tracked through the FBI's reporting center have climbed year after year, and customers read that news too, which means every online business now serves an audience arriving warier than the one it designed its flows for.
Customer trust also moves faster than fraud statistics. One viral story about a frozen account reaches more prospective customers than a year of clean operation, so the experience around every block carries reputational weight far beyond the single transaction it touches.
Wariness changes behavior before any attack does. Shoppers abandon checkouts that feel off, hesitate at unfamiliar payment screens and judge unexpected verification requests harshly, so the perception of risk taxes conversion even when the actual defenses hold perfectly.
Acquisition spend makes the stakes concrete. A business paying real money per new customer loses the whole investment when a clumsy first verification scares that customer off, which prices the onboarding friction in the same currency as the media budget.
That makes the fraud program a revenue instrument with two blades. It protects margin by stopping losses, and it protects growth by making legitimate customers feel safe rather than suspected, and programs measured only on the first blade reliably dull the second.
None of this argues for softer defenses. It argues for smarter spending of the friction the defenses require, and the distinction is the difference between a security program and a customer trust program that happens to stop fraud.
The organizational fix is a shared scorecard. When the fraud team, the growth team and the support team read the same numbers, approval rates and complaint themes beside loss figures, the trade-offs get made deliberately instead of by whichever team shouted last.
Customer trust is the asset all three teams are managing. It accumulates through hundreds of uneventful logins and spends itself in one badly handled block, which is why the rest of this playbook concentrates on the moments where the controls become visible.
Proportionate Friction Protects Customer Trust
The working principle is proportionality. A recognized customer on a familiar device doing ordinary things should feel almost nothing, while a new device, an unusual location and a sensitive account change together justify checks that would insult the first customer, and the system's intelligence shows in telling them apart.
Progressive trust is the pattern customers accept most readily. New accounts start with modest limits and light history, and room grows as behavior accumulates, which matches how customer trust works in the other direction too, earned in layers rather than granted at sign-up.
Flat friction is the lazy failure mode. Applying the same heavy verification to every login treats returning customers like suspects on every visit, and the loyalists who log in daily pay the highest cumulative tax for behavior that should have earned them the lightest touch.
Session continuity is part of the bargain. A customer who passes a check should not meet the same check twice in an hour, and a system that remembers its own decisions reads as competent, which is where customer trust starts.
Verification steps are interface design, not just policy. The way a challenge appears, how many actions it demands and whether it preserves the customer's progress decide its real cost, and thoughtful interaction design of those states, clear fields, saved carts and sensible retry behavior, cuts the friction without cutting the protection.
The loyal-customer experience deserves its own review. The people who log in daily generate the cleanest signals and earn the least friction, and designing an explicitly smoother path for them turns the security system into a quiet loyalty benefit that deepens customer trust instead of taxing it.
Timing shapes perception as much as volume. A check that arrives before a customer invests effort reads as diligence and spends almost no customer trust, while the same check appearing after a completed form feels like a trap, so high-risk verification belongs as early in the flow as the signals allow.
Accessibility applies to security steps too. Checks that assume one device type, sharp eyesight or perfect English quietly exclude paying customers, and the audit of who cannot complete a verification is also a map of revenue the controls are leaving outside.
Customers do not need the risk math explained. They need the response to feel reasonable for what they just did, and reasonable is a design standard a team can test for, not a compliance abstraction.
Explanations Are Conversion Copy
A declined action with no explanation is the worst message a platform sends all day. The words around security events decide whether the customer blames the fraudster, the bank or the brand, and a bare transaction-failed error reliably picks the worst of the three.
The pattern for trust-building responses is consistent across situations.
- New-device login. Ask for the extra step and say plainly why it appeared
- Payment under review. Say a security check is running and what happens next
- Password or detail change. Confirm it immediately through a second channel
- Suspicious activity. Alert the customer before they discover it themselves
- Repeated rejection. Offer a human escalation path instead of another loop
Plain wording carries the whole pattern. The federal plain language guidelines exist for exactly this kind of writing, short sentences, familiar words and the next step stated once, because a stressed customer reads security messages at their worst and quits at the first confusing line.
Second-channel confirmations multiply the effect cheaply. A short notice after any sensitive change gives the legitimate customer visibility and the compromised one an early alarm, and the same message serves both without a single extra control in the flow.
Companies never need to publish their detection rules, and the secrecy is compatible with clarity. The message explains what the legitimate customer should do next, not how the system decided, and that boundary protects the defenses while still treating the person as a customer rather than a case number.
Support scripts belong inside the same system. The agent answering a blocked-payment call needs language consistent with the on-screen message and authority to resolve the case, because customer trust collapses fastest in the gap between what the screen said and what the phone call reveals.
Voice belongs to the brand even here. A documented brand positioning that extends into security and service messages keeps the scariest moments sounding like the same company as the marketing, and the continuity itself reassures, because fraudsters imitate logos far more easily than they imitate a consistent voice.
Message timing has a courtesy dimension. Security alerts sent at 3 a.m. for routine events train customers to ignore the channel, so urgency tiers decide what wakes a person and what waits for morning, and the channel stays credible for the day it matters.
Consistency compounds into customer trust. When customers learn that this platform always explains, always confirms and always alerts, the occasional extra check reads as the system working, which is the quiet payoff of treating security copy as seriously as campaign copy.
Layered Signals Beat Single Triggers
One odd event is weak evidence. Customers travel, replace phones, use new cards and spend unusually before holidays, and a system that blocks on any single anomaly punishes ordinary life while barely inconveniencing a practiced attacker.
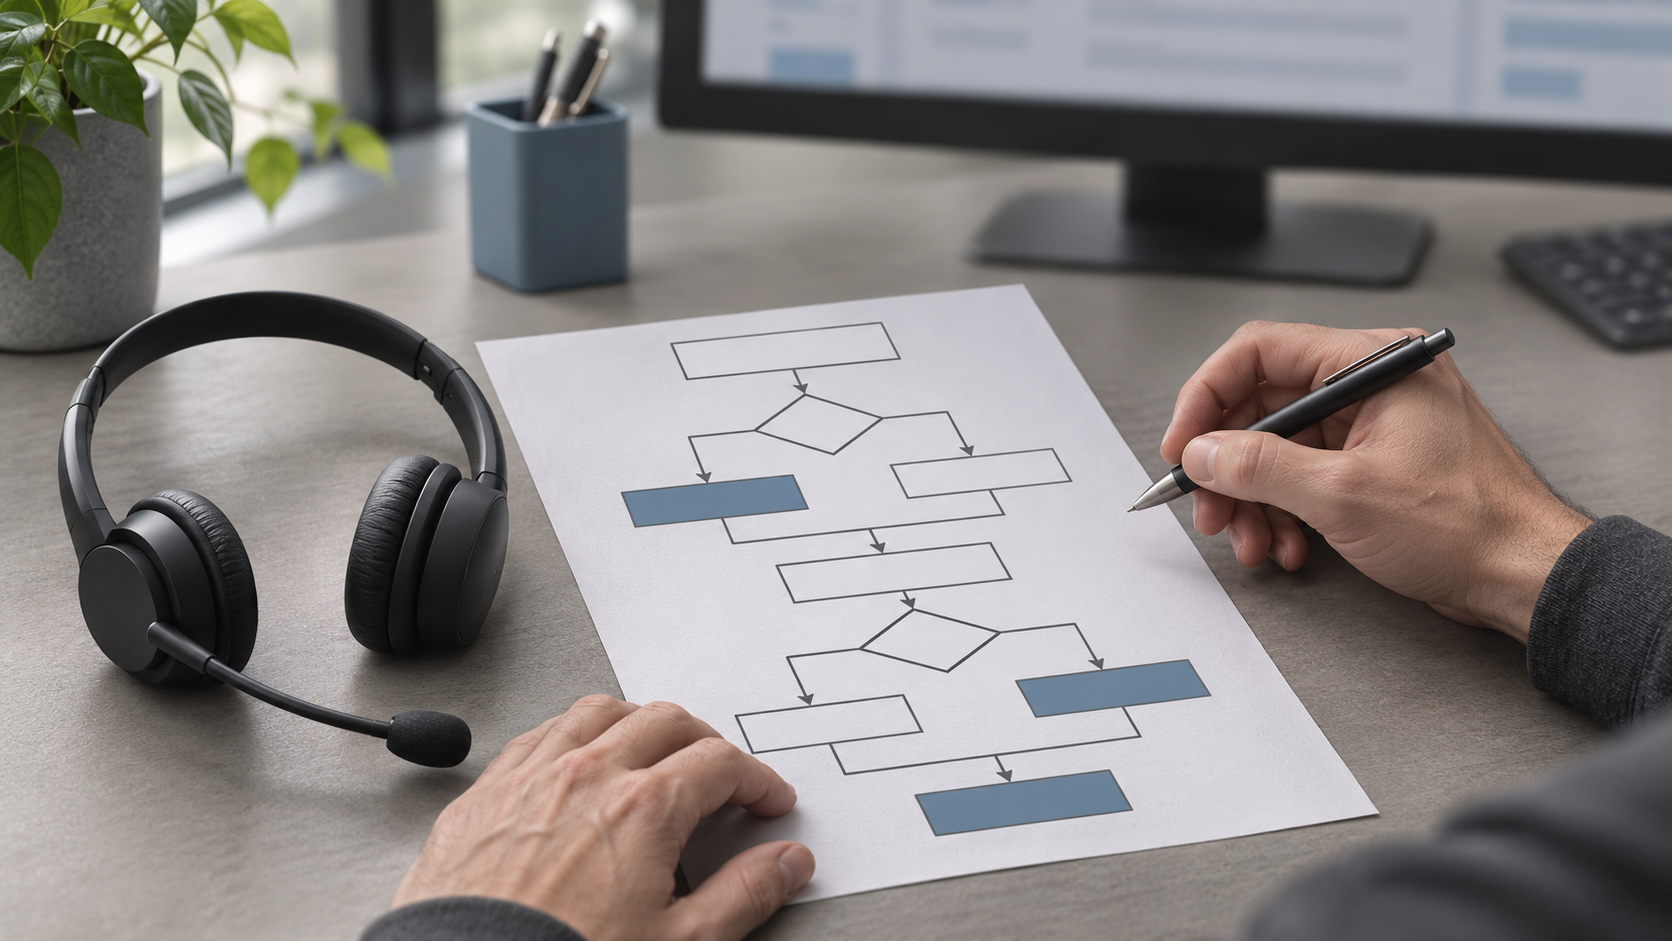
Modern programs read combinations instead. Guidance on fraud prevention strategies from platforms such as Frogo describes layering identity verification, authentication, device intelligence, behavioral analytics and continuous risk scoring, and the layering is the point, context turns the same signal from noise into evidence.
The customer trust consequence is precision. A layered read lets the platform wave through the traveler with a new phone and tighten only around the genuinely strange pattern, which spends friction where it buys protection and nowhere else.
Rules need pruning as much as adding. Controls accumulate from old incidents and stay long after the threat pattern fades, so a periodic review that retires stale rules returns friction to customers who never deserved it and usually costs nothing in protection.
Internal controls belong in the same architecture. Access limits, approval workflows and activity logs reduce the risks customers never see, and outward customer trust is only as durable as the operation behind it, since a calm login screen means little if sensitive data moves loosely behind the curtain.
Thresholds deserve seasonal sense. Holiday spikes, launch days and promotion windows produce exactly the unusual behavior that static rules flag, and a program that loosens the right screws on its biggest revenue days protects the quarter instead of its own averages.
Vendor choices deserve the same proportionality test the flows get. The practical question for any tool is which legitimate-customer behaviors it will misread and how its decisions get explained, appealed and corrected, because the platform, not the vendor, answers to the customer the model gets wrong.
False Positives Are Silent Churn
Fraud teams count what gets through, while customers count what gets blocked. The legitimate buyer whose payment fails twice does not file a fraud-model complaint, they conclude the site is broken and buy elsewhere, and the loss lands in revenue reports where nobody tags it as a security cost.
Measurement closes that visibility gap. Approval rates, false-positive counts, review queue times and the share of customers who hit extra checks belong beside the loss figures, and a program that tightens controls without improving detection shows up immediately in that fuller set.
The support queue is the fullest false-positive dataset a team owns. Tickets about blocked payments and locked accounts, tagged and counted by flow, show precisely where the controls misfire on real customers, and the tagging costs a dropdown.
Friction concentrates unevenly, which makes fairness a metric too. Certain regions, devices and customer profiles draw more challenges than others, and a platform that never checks who carries the burden can drain a whole segment's customer trust while its averages look healthy.
Customer trust research rounds out the numbers. Asking recent customers how safe the experience felt, and asking lapsed ones what pushed them out, attaches reasons to the approval-rate curves and regularly surfaces a friction point the analytics never isolated.
A structured UX audit of the security touchpoints finds what the dashboards summarize. Walking the flows as a new customer, a returning customer and a flagged customer surfaces the dead ends, the lost carts and the unexplained blocks exactly as real users meet them, and the findings usually pay for the exercise in the first fixed flow.
Recovery design is the half of false-positive work most teams skip. Every wrongly blocked customer needs a fast, human-reachable path back to normal, because the block itself costs a transaction while a bad recovery costs the customer trust behind the account.
After the Incident, the Brand Speaks
No program prevents everything, and customers largely know it. What they grade is the response, how fast the account gets protected, how clearly the company explains what happened and who owns the follow-up, and that grade usually outweighs the incident itself in the renewal decision.
Silence is the one unforgivable choice. A customer who reports something suspicious and hears nothing concludes the company is not in control, and public guidance on consumer fraud teaches people to expect prompt, concrete steps, which sets the bar any brand response gets measured against.
Proactive disclosure beats discovered silence even when the news is bad. Customers forgive the platform that told them first far more readily than the one they caught, and the first-mover advantage on bad news is one of the few the brand fully controls.
Preparation is what makes speed possible. A drafted communication plan, a named owner and rehearsed escalation paths decide whether the first customer email goes out in an hour or a week, and the difference is written long before anything goes wrong.
Consumer platforms carry the widest exposure here. Teams running consumer marketing programs know a mishandled incident travels through reviews and social feeds at campaign speed, while a well-handled one quietly becomes a retention story, the protected, informed and restored customer tells that version too.
The post-incident review feeds the whole loop. Which signals fired late, which messages confused people and which customers churned afterward turn one bad day into next quarter's improvements, and the discipline of running that review is itself a difference customers eventually feel.
Customer Trust Is the Real Control
Fraud programs earn their budgets twice, once in the losses they stop and once in the customer trust they preserve while stopping them. Proportionate friction, explanations written like conversion copy, layered signals, honest false-positive accounting and a rehearsed response close the gap between a secure platform and one that feels secure.
The businesses that win warier markets treat those as the same project. Security that respects the legitimate customer at every visible moment turns a cost center into a reason to stay, and customer trust, once it compounds, is the one defense a competitor cannot copy at any price.